These days, almost every application is built using a mix of dozens, and sometimes even hundreds, of third-party and open-source components. Without a clear understanding of what’s actually inside your software, it can be difficult to catch potential risks.
That’s where a Software Bill of Materials (SBOM) comes in handy. It provides a comprehensive, organized list of every component in your application, making it easier to identify vulnerable dependencies and keep track of licensing obligations.
With a wide range of tools now offering SBOM capabilities, we’ve covered the top 9 platforms that are definitely worth your attention. Below, we explore their key features and explain how SBOM generation works.
Top 9 SBOM Tools to Simplify Audit and Compliance
|
Platforms |
SBOM Formats |
Continuous Monitoring |
|
Aikido |
CycloneDX, SPDX, CSV |
✅ |
|
Snyk |
SPDX |
✅ |
|
JFrog Xray |
N/A |
✅ |
|
Sonatype |
CycloneDX, SPDX |
✅ |
|
FOSSA |
CycloneDX, SPDX |
✅ |
|
Black Duck |
N/A |
✅ |
|
Mend.io |
CycloneDX, SPDX |
✅ |
|
Anchore |
CycloneDX, SPDX |
✅ |
|
Veracode |
CycloneDX, SPDX |
✅ |
Aikido
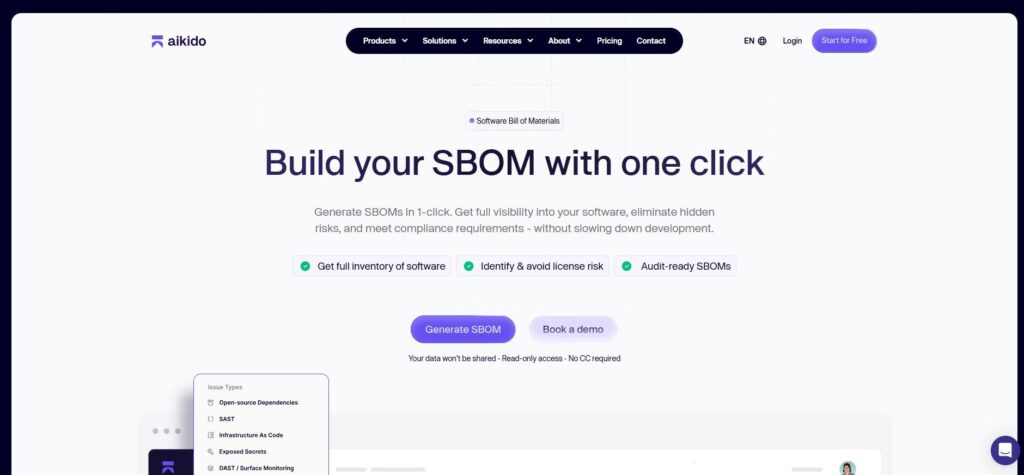
Aikido is a platform built to give users full visibility into the software they build and use. It covers things like dependency scanning, container checks, and code analysis, securing code, cloud, and runtime. It is not a one-time scan, but rather continuous monitoring for things like vulnerable open-source dependencies, outdated or unmaintained software, malicious packages, or container image risks.
SBOM Generation: The process starts by connecting your code repositories and giving access to the projects you want reviewed. Then, the system goes through your licenses and flags the risk level tied to them, so you can see at a glance which dependencies might cause legal or compliance issues. Once the review is done, you can export the SBOM in your preferred format, CycloneDX, SPDX, or CSV, all with a single click.
It goes further by adding a few extra layers. Each component listed comes with clear copyright information pulled automatically, saving legal teams from having to dig through source code themselves. You can also adjust how license risk is scored and mark certain licenses as internal so they don’t clutter your report. Unlike many SBOM tools that only look inside code repositories, Aikido also scans containers, giving broader coverage.
Snyk
Snyk is an AI security platform that checks and secures AI-generated code, AI agents, and native applications. It works inside tools teams already use, like IDEs, CI/CD pipelines, and AI coding assistants like Claude Code, Cursor, and Codex.
SBOM Generation: Snyk scans a project’s package manifests to build a dependency graph, which shows vulnerabilities and outdated packages. To transform this graph into a complete SBOM, Snyk uses community tools like snyk2spdx. This open-source project takes the output from the Snyk CLI and converts it into the SPDX format, which is the standard for SBOMs.Developers can also use the Snyk API to pull package and vulnerability data and convert it to SPDX themselves.
Snyk also offers an auditing feature that creates a searchable SBOM report, and a tool called Snyk Advisor that scores how healthy and well-maintained each package is, helping users pick safer libraries to use.
JFrog Xray
JFrog is a software supply chain platform that gives teams one central place to manage, secure, and deliver software and AI assets. It brings together artifact management, security scanning, and governance in a single system, making it easier for DevOps, security, and ML teams to work from the same source of truth.
SBOM Generation: JFrog Xray creates a Software Bill of Materials (SBOM) through four key steps. First up, it scans all artifacts to identify every software component, whether it’s source code or binaries, across the various technologies it supports. Next, it extracts important metadata for each component, such as license information, package identifiers, and the relationships between components. After that, it cross-references each component with JFrog’s proprietary database, using details like hashes, component IDs, architecture, and distribution information to accurately identify each piece. Finally, the finished SBOM is stored in Xray’s database, making it simple to access, manage, and export whenever needed.
Sonatype
Sonatype is a platform built to help engineering teams control what goes into their software, whether that’s open source components, containers, AI models, or SBOMs. It gives developers and AI agents the intelligence to choose safe components, block risky ones, and fix all the issues before they reach production.
SBOM Generation: Sonatype SBOM Manager automates SBOM generation and monitoring, ensuring they’re always ready for an audit. It supports both CycloneDX and SPDX formats, and can pull SBOMs from multiple sources through APIs to keep them accurate and current across the SDLC. Apart from generation, it continuously tracks components for new vulnerabilities, malware, and license issues, and includes VEX annotations so users can see the real-world exploitability of any flagged vulnerability. Plus, it offers license obligation management with a handy built-in checklist workflow, allowing legal and compliance teams to tackle licensing issues more quickly while maintaining a complete version history for easy traceability.
FOSSA
FOSSA is a platform built to give organizations control over their software supply chain, covering license compliance, security, and SBOM management for all third-party code they use.
SBOM Generation: FOSSA covers the full SBOM lifecycle. It can generate detailed SBOMs that identify every dependency in a project, going as deep as needed. It can also produce SBOMs for older versions of the software, along with the current ones. Teams can export in formats like CycloneDX and SPDX, then either download and share the file themselves, or let FOSSA host and distribute it for them. Every SBOM stays updated through an auto-update feature, and everything is stored in one central place with access controls. It also connects into CI/CD pipelines through GitHub and GitLab integrations.
Black Duck
Black Duck is an application security platform that offers a full range of testing tools, all built to secure code across the entire development lifecycle. Beyond scanning proprietary code, Black Duck also focuses heavily on third-party and open-source components, tracking their versions, licenses, and security status to help organizations stay compliant with supply chain regulations.
SBOM Generation: Black Duck’s SCA analysis tools use advanced detection models to create and manage SBOMs, giving full visibility into every open source and third-party component inside an application. It tracks the version, license, and security status of each component to keep the SBOM accurate. The platform also extends SBOM coverage to AI models used within applications. With its AI Model Risk Insights feature, it can detect AI models embedded in software and surface details like their versions, licenses, and associated risks.
Mend.io

Mend.io is a security platform covering application and AI security and designed to protect code, AI systems, and everything in between.
SBOM Generation: SBOM generation at Mend.io is handled through Mend SCA, which automatically produces accurate SBOMs in both SPDX and CycloneDX formats. Within its SBOM solutions, it covers advanced reachability analysis, risk-based prioritization, malicious package protection, and holistic policy automation. It keeps SBOMs updated as dependencies change across all applications. It also incorporates VEX data and integrates third-party SBOMs to keep software secure and compliant.
Anchore
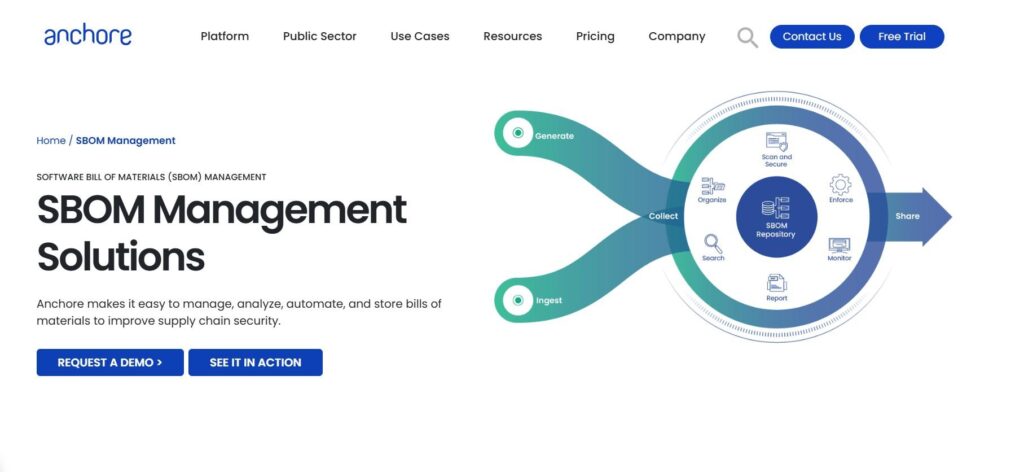
Anchore is a company focused on software supply chain security, particularly for cloud-native and container-based environments.
SBOM Generation: Anchore SBOM lets teams manage internal and third-party SBOMs, as well as track supply chain issues. It supports uploading SBOMs in standard formats like SPDX and CycloneDX, and can also generate SBOMs natively for containers as part of CI/CD, registry, or runtime scanning. Once SBOMs are in the system, Anchore scans them for vulnerabilities and applies its own scoring system, called Anchore Score, which combines CVSS, EPSS, and KEV data into one number. This helps users see which vulnerabilities matter most and prioritize fixing those first.
Veracode
Veracode is an application risk management platform built to identify security risks across the software development lifecycle as well as simplify governance and compliance.
SBOM Generation: Veracode handles SBOM creation and scanning through its Software Composition Analysis (SCA) product, supporting both CycloneDX and SPDX formats. Users can generate an SBOM either through the REST API based on an existing SCA scan or directly during an SCA agent-based scan. To maintain flexibility, teams have the option to set up scans that target only SBOM files, completely bypass them, or even merge SBOM data with a comprehensive static analysis scan, based on their specific needs at any point in the development process.
Final Thoughts
When it comes to choosing the right SBOM platform, it’s all about finding a tool that fits your organization’s needs, whether that’s staying compliant with regulations, managing licenses, or tracking vulnerabilities.
For businesses that want to tackle all these aspects, Aikido is a solid starting tool. It not only generates SBOMs but also includes built-in analysis for open-source licenses, giving your legal and security teams a clear view of potential risks without the hassle of juggling data from different tools.
This way, your SBOM stays accurate, and your organization is always ready for an audit.